// about
Senior security judgement, built into every project.
XIVU is led by Chan Vu Luu. For seven years he worked in information security for one of Germany’s largest car manufacturers, one of Germany’s largest banks, a financial IT service provider, one of Germany’s largest federal agencies and one of Germany’s largest enterprise software companies. Today he builds and secures digital products for companies that cannot afford to get it wrong.
// the founder
The founder
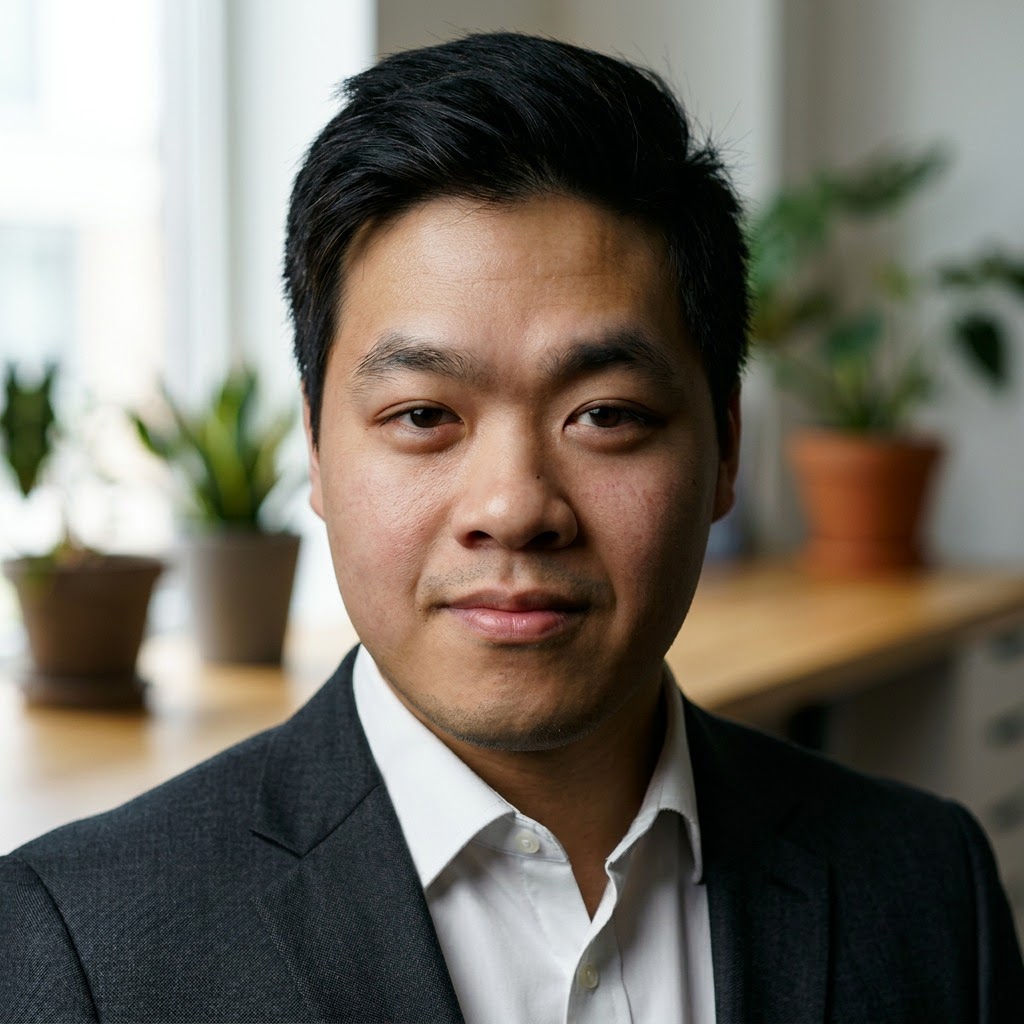
Chan Vu Luu
Founder & CEO
Chan Vu Luu is the founder of XIVU, a software studio in Fürth, Germany. He is a former Deputy Information Security Officer with an ISO/IEC 27001:2022 Lead Auditor qualification (TÜV NORD, CQI/IRCA-certified course) and seven years of ISMS audits, risk analyses and supplier audits. Today he builds software with security by design and a secure SDLC, and he built NIUJU, XIVU’s own AI photo studio.
Chan Vu has sat on both sides of the audit table. As a consultant, he assessed other companies’ security. As Deputy Information Security Officer, he was the one being audited. That is why he knows what auditors look for, what enterprise customers ask before they sign, and which shortcuts come back to hurt you a year later.
His job was always the same: find the weak spot before someone else does, and explain it so that leadership can make a clear decision.
His internal audits have one purpose: find every gap before the external auditor does, and turn each one into a measure that holds up. Not a sample, not a box-ticking exercise, the whole picture.
Companies also trusted him to build up their security people. He trained newly appointed Information Security Officers, at his own employer and at a federal agency, and brought them up to speed on the ISMS, audits and day-to-day security work.
// the record
What he has delivered.
- 12 supplier audits in two months for one of Germany's largest banks, clearing a backlog of reviews that had built up over years. Each one measured against the bank's own control catalogue, with interviews, evidence requests, findings and a clear recommendation.
- Seven years of ISMS audits, risk analyses and supplier audits under ISO 27001, TISAX, BSI IT-Grundschutz and BSI C5: as a consultant for one of Germany's largest car manufacturers, a financial IT service provider, one of Germany's largest banks, one of Germany's largest enterprise software companies and a federal agency, and in-house as Deputy Information Security Officer.
- Internal BSI C5 audits of the cloud services of one of Germany's largest enterprise software companies: are the controls in place, and do they actually work?
- Audit readiness restored at one of Germany's largest federal agencies. He took over a running ISMS mandate shortly before the external audit and brought the department back to audit readiness.
- External TISAX and ISO 27001:2022 audits passed by his own employer, with Chan Vu as Deputy Information Security Officer contributing directly.
- Access rights for banking software. At a direct bank he was responsible for identity and access management (IAM) for its banking applications: defining, reviewing and implementing role and rights concepts with the business units, as deputy lead of a 20-person IT team.
- Earlier: IT project work at a leading European truck and bus manufacturer.
// what a supplier audit covers
He checks how your suppliers really work, not what their brochure says.
When a cloud provider, software vendor or service partner gets access to your data, their weak spot becomes yours. In third-party risk management, Chan Vu audited suppliers for large enterprises across the whole security picture:
- Policies and governance: do written security rules exist, are they current, and does anyone follow them?
- Security management: is there a working ISMS with risk management, responsibilities, internal audits and real follow-up on findings?
- Identity and access management: who can access what, how rights are granted and removed, and how admin access is controlled.
- Data protection: technical and organisational measures (TOMs) under the GDPR, data processing agreements, where data is stored and who processes it.
- Technical security: cloud and hosting setup, encryption, logging and monitoring, patching and vulnerability handling.
- Evidence, not promises: certificates and attestations (ISO 27001, TISAX, BSI C5) checked for scope and validity, plus documents, interviews and samples where a certificate does not cover the risk.
The result is always a clear decision: sign, sign with conditions, or do not sign.
- 7 yearsin information security
- 5 industriesautomotive, banking, financial IT services, enterprise software, public sector
- Both sidesconsultant and in-house Deputy Information Security Officer
- IT since 2011IT specialist apprenticeship at TU Darmstadt, 2011 to 2014
// why clients pay for this
You are not paying for a checklist.
Anyone can fill in a security checklist. What you pay for is knowing which three points on it matter for your business, and which risk will cost you the deal, the audit or the customer.
- Faster decisions. You hear what matters, in plain language, with clear options and a recommendation.
- Fewer expensive surprises. One unreliable supplier, one data leak or one audit finding that blocks a sale costs more than a year of good advice.
- Work that holds up. Documentation and evidence built to the standard auditors and enterprise buyers expect, aligned with ISO/IEC 27001, BSI IT-Grundschutz, BSI C5 and TISAX.
- One accountable person. No junior learning on your budget. The person you meet is the person who does the work.
// how to work with chan vu
How to work with Chan Vu.
- Security Partner for your projectfrom €1,100 per day
- Supplier Security Checkfrom €3,900 per supplier
- Security Readiness Reviewfrom €5,900
- Secure Launch
we build it, secured from day onefrom €12,900
All services are for business customers only. Prices net, plus VAT.
// proof: our own product
We build our own product the same way.
NIUJU, our AI photo studio, handles personal photos every day. Photos are stored in the EU, deleted automatically 7 days after upload and never used to train AI. Every change that touches personal data, accounts or payments passes security, privacy and payment reviews before it goes live.
// honest by default
We only claim what we can prove.
We build with the GDPR in mind and bring years of hands-on experience with information security and data protection requirements. We do not advertise certificates we do not hold: XIVU itself is not ISO 27001 certified and holds no GDPR certification. Our qualifications are personal, and we name them precisely.
Qualifications
- ISO/IEC 27001:2022 Lead Auditor qualification (TÜV NORD, CQI/IRCA-certified course)
- COBIT 5 Foundation
- ITIL Foundation
- Professional Scrum Master (PSM I)
“For years my job was to ask companies one question: can you prove it? Now I make sure my clients can always answer yes.”